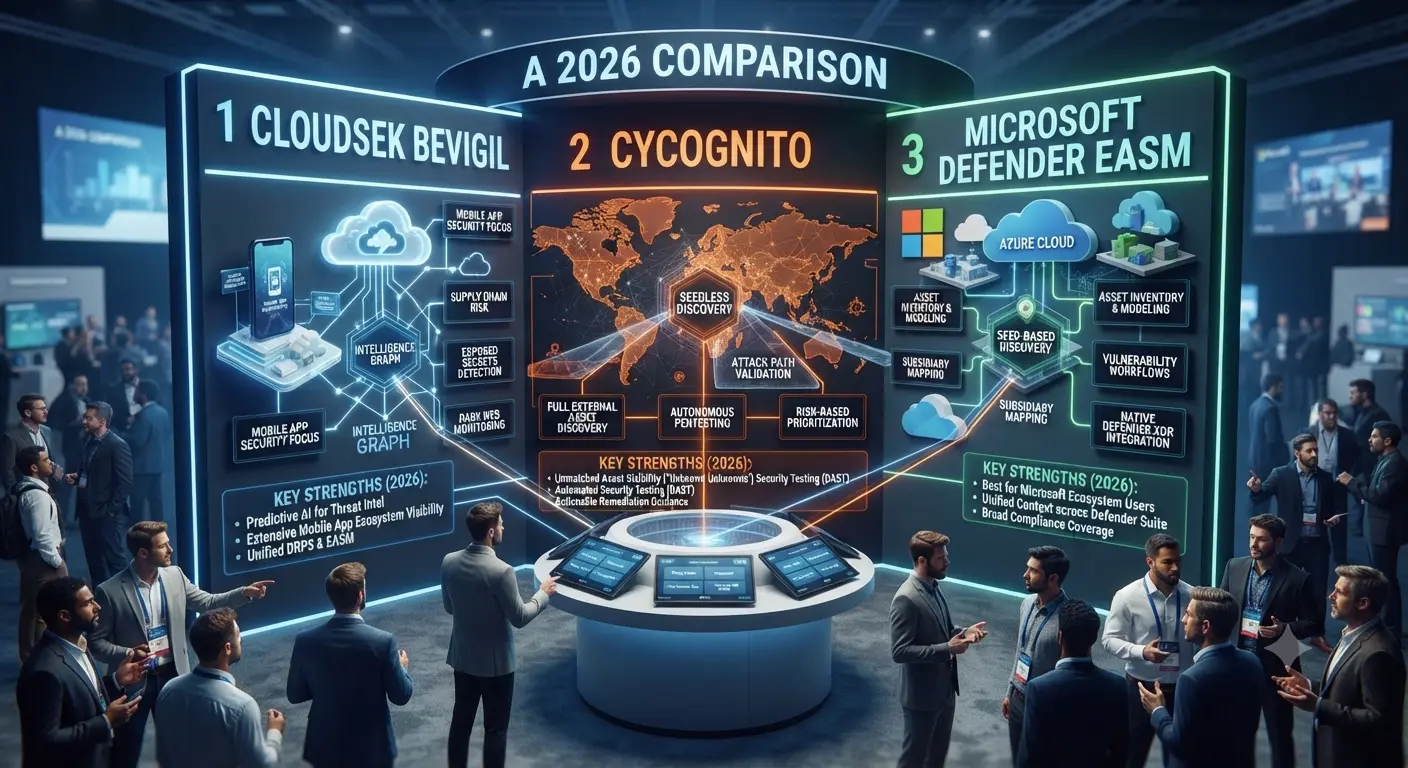
CloudSEK BeVigil, CyCognito, and Microsoft Defender EASM are external attack surface management (EASM) platforms that help organizations discover internet-facing assets and find security exposures before attackers do. They differ in how they discover assets, how they confirm exposures, and how they decide what to fix first.
The stakes are rising. Verizon’s 2026 Data Breach Investigations Report found that exploitation of vulnerabilities was the most common initial access vector, at 31% of breaches. Only 26% of critical vulnerabilities in CISA’s Known Exploited Vulnerabilities catalog were fully remediated, with a median of 43 days to fix. EASM platforms help security teams find these exposures and judge their impact as part of broader cybersecurity risk management.
This comparison examines the features, capabilities, and use cases of BeVigil, CyCognito, and Microsoft Defender EASM to help you decide which platform fits your security requirements.
CloudSEK BeVigil vs CyCognito vs Microsoft Defender EASM: Quick Comparison
| Comparison | BeVigil | CyCognito | Microsoft Defender EASM |
| Vendor | CloudSEK, founded in 2015, headquartered in Singapore | CyCognito | Microsoft, built on its 2021 RiskIQ acquisition |
| Primary focus | External attack surface monitoring across eight attack surfaces | External exposure management with active testing | External asset discovery and inventory |
| Asset discovery | Continuous discovery and fingerprinting of known, forgotten, and shadow IT assets | Seedless discovery with attribution to subsidiaries, brands, and acquisitions | Recursive discovery from seeds such as domains, IP blocks, hosts, ASNs, and WHOIS organizations |
| Exposure detection | Web, mobile, API, cloud, network, DNS, SSL/TLS, and CVE exposures, including SPF and DMARC issues, subdomain takeovers, and secrets in code | Exposures confirmed through automated active security testing | Vulnerabilities and security hygiene issues across discovered infrastructure |
| Risk prioritization | 600+ classifiers weigh reachability and exploitability; Nexus AI ranks exposures that sit on attack paths | Exploitability, business context, and threat intelligence | Asset insights, severity, and security dashboards |
| Attack path context | Nexus AI correlates BeVigil findings with CloudSEK’s dark web, threat actor, AI, and vendor signals | Links validated exposures to business context | Maps external infrastructure and related risks |
| Ecosystem | CloudSEK platform with 50+ integrations | Security and vulnerability management integrations, including Wiz | Microsoft Defender for Cloud, Security Exposure Management, and Microsoft Sentinel |
| Best suited for | Organizations that need multi-surface visibility tied to attack path context | Enterprises that want seedless discovery and active validation | Organizations standardized on Microsoft security tools |
1. BeVigil by CloudSEK
BeVigil is CloudSEK’s external attack surface monitoring platform. It fingerprints an organization’s internet-facing infrastructure and continuously scans it for misconfigurations, vulnerabilities, and exploitable initial access vectors. CloudSEK, the AI-native predictive cyber intelligence platform behind BeVigil, was founded in 2015 and is headquartered in Singapore.
BeVigil answers one question for security teams: what does our external attack surface look like, and where are the exploitable initial access vectors? It does this across eight attack surfaces rather than relying only on domain or IP-based monitoring, then uses Nexus AI to show how separate exposures could combine into an entry route.
Key features:
- Automated asset discovery. Continuously discovers and fingerprints domains, subdomains, open ports, web and mobile applications, SSL certificates, and network devices, including forgotten and shadow IT infrastructure.
- Eight attack surfaces. Scans web applications for SQL injection, cross-site scripting, and business logic flaws; mobile apps for OWASP Mobile Top 10 issues, cloud leaks, and hard-coded secrets; APIs for broken authentication and data exposure; cloud for exposed storage buckets and open management portals; network for exposed services and unpatched appliances; DNS for SPF and DMARC issues and subdomain takeovers; SSL/TLS for weak ciphers and certificate problems; and external systems against known CVEs.
- Exposure coverage. CloudSEK says BeVigil covers more than 1,900 web application exposure types, 500 cloud security issues, and 200 initial access vectors.
- Noise reduction. More than 600 tag classifiers and query-language filters weigh reachability and exploitability, so teams focus on exposures attackers can actually use.
- Attack path correlation. Nexus AI, CloudSEK’s attack path intelligence layer, promotes exposures that sit on a potential attack path to the top and correlates them with CloudSEK’s dark web, threat actor, AI attack surface, and vendor signals.
- Continuous checks and re-testing. Daily security checks pick up new assets as they appear, with automatic re-testing after fixes.
- Integrations and tools. Connects to 50+ security tools through APIs, with free tools including a Mobile App Analyser and BeVigil Asset Explorer.
Consider: CloudSEK does not publicly describe BeVigil’s discovery as seedless, so test discovery depth against your own asset inventory during a proof of concept.
Best for: Organizations that need continuous monitoring across web, mobile, API, cloud, and network assets, with visibility into how separate exposures connect into attack paths.
2. CyCognito
CyCognito is an external exposure management platform that discovers internet-facing assets and validates security exposures through active testing. It uses seedless discovery to map external infrastructure without a starting list of known assets, and attributes what it finds to the right subsidiaries, brands, and business units.
Key features:
- Seedless discovery. Maps an organization’s external footprint across SaaS, cloud, and on-premises environments without manual input. CyCognito claims this uncovers up to 20 times more assets than other tools.
- Asset attribution. Automatically attributes shadow IT, acquired companies, and subsidiary assets to the right part of the business.
- Active security testing. Runs automated security tests against discovered assets to confirm whether weaknesses are exploitable. CyCognito cites more than 100,000 testing modules.
- Exploitability-based prioritization. Ranks issues by exploitability, business context, and threat intelligence rather than raw severity scores.
- Integrations. Connects with security and vulnerability management tools, including a Wiz integration for black-box discovery and dynamic application security testing.
Consider: Active testing generates traffic against your assets, so confirm scope, scheduling, and change-control processes before rollout.
Best for: Large enterprises with complex subsidiary structures that want broad discovery, active exposure validation, and risk-based prioritization.
3. Microsoft Defender External Attack Surface Management
Microsoft Defender External Attack Surface Management (Defender EASM) helps organizations discover and manage internet-facing assets, including infrastructure that internal security tools may not track. It is built on technology from RiskIQ, which Microsoft acquired in 2021.
Key features:
- Seed-based recursive discovery. Starts from known assets, called discovery seeds, such as domains, IP blocks, hosts, email contacts, ASNs, and WHOIS organizations, then recursively finds connected infrastructure.
- Discovery groups. Groups seeds into discovery runs that can repeat on a schedule, with exclusions to keep unrelated entities out of the inventory.
- Inventory and dashboards. Provides asset inventories and dashboards covering vulnerabilities, compliance, and security hygiene, including GDPR compliance and OWASP Top 10 views.
- Microsoft ecosystem integration. Feeds insights into Microsoft Defender for Cloud and Microsoft Security Exposure Management, and integrates with Microsoft Sentinel.
Consider: Discovery quality depends on the seeds you provide. Full dashboards and custom discovery groups require a standalone Defender EASM workspace, even where Defender for Cloud surfaces some EASM insights.
Best for: Organizations standardized on Microsoft security tools that want external asset discovery inside the same ecosystem.
Key Differences Between BeVigil, CyCognito, and Microsoft Defender EASM
All three platforms provide external attack surface visibility, but they differ in four areas.
1. Asset Discovery
BeVigil continuously discovers and fingerprints assets across eight attack surfaces, including mobile apps and APIs. CyCognito uses seedless discovery and organizational attribution to find assets linked to subsidiaries, brands, and acquisitions. Microsoft Defender EASM starts with known seeds and recursively discovers related infrastructure.
2. Coverage Beyond Web Infrastructure
BeVigil treats mobile applications as a dedicated attack surface, scanning for OWASP Mobile Top 10 issues and hard-coded secrets, alongside APIs and cloud services. CyCognito covers external assets across SaaS, cloud, and on-premises environments. Microsoft Defender EASM focuses on domains, hosts, IP blocks, and related infrastructure.
3. Exposure Detection and Validation
BeVigil identifies vulnerabilities and misconfigurations, re-tests after fixes, and validates attack paths through Nexus AI. CyCognito emphasizes active security testing to confirm whether weaknesses are exploitable. Microsoft Defender EASM surfaces vulnerabilities and hygiene issues through its inventory and dashboards.
4. Risk Prioritization
BeVigil uses its classifiers and Nexus AI to put exposures that sit on attack paths first. CyCognito combines exploitability, business context, and threat intelligence. Microsoft Defender EASM offers asset insights and dashboards for teams to investigate.
In short, BeVigil suits teams that want multi-surface monitoring tied to attack path context, CyCognito suits enterprises that prioritize seedless discovery and active validation, and Microsoft Defender EASM suits organizations that want EASM inside the Microsoft ecosystem.
How to Choose the Right EASM Platform
When selecting an EASM platform, evaluate how well it supports your infrastructure, security workflows, and security investigation processes. Key factors include:
- Asset coverage. Support for web applications, mobile apps, APIs, cloud, and network assets.
- Discovery method. Seedless, seed-based, or continuous fingerprinting, and how well it finds assets you do not already know about.
- Exposure validation. The ability to verify exploitability and re-test after remediation.
- Risk prioritization. Context based on exploitability, business impact, and attack paths.
- Integrations. Compatibility with your SIEM, vulnerability management, and ticketing tools.
- Reporting and scale. Clear remediation guidance and support for growing infrastructure.
Before buying, run a proof of concept that compares discovery accuracy against your own asset inventory, checks how each platform validates exposures, and tests integration with your existing workflows.
Frequently Asked Questions
What is external attack surface management (EASM)?
EASM is the continuous discovery and monitoring of an organization’s internet-facing assets, such as domains, applications, APIs, and cloud services, to find exposures attackers could exploit.
What is the difference between seedless and seed-based discovery?
Seed-based discovery starts from assets you already know, such as domains and IP ranges, and expands from there. Seedless discovery maps an organization’s footprint without a starting list, which can surface assets from subsidiaries or acquisitions that no one recorded.
What is active security validation in EASM?
Active validation runs safe tests against discovered assets to confirm whether a weakness is actually exploitable, which reduces false positives and helps teams focus on real risk.
Is Microsoft Defender EASM included with Defender for Cloud?
Defender for Cloud can surface some EASM insights, but full Defender EASM dashboards, custom discovery groups, and Security Exposure Management integration require a standalone Defender EASM workspace.
What is CloudSEK BeVigil and how does it monitor the external attack surface?
BeVigil is CloudSEK’s external attack surface monitoring platform. It continuously discovers and fingerprints internet-facing assets, scans eight attack surfaces (web, mobile, API, cloud, network, DNS, SSL/TLS, and CVE) for exploitable initial access vectors, and uses Nexus AI to rank the exposures that sit on potential attack paths.